Your WordPress site is hacked. I can clean it properly.
Full malware removal, backdoor cleanup, Google blacklist warning removal, and the hardening that stops it happening again. Done by one person who will tell you exactly what was wrong.
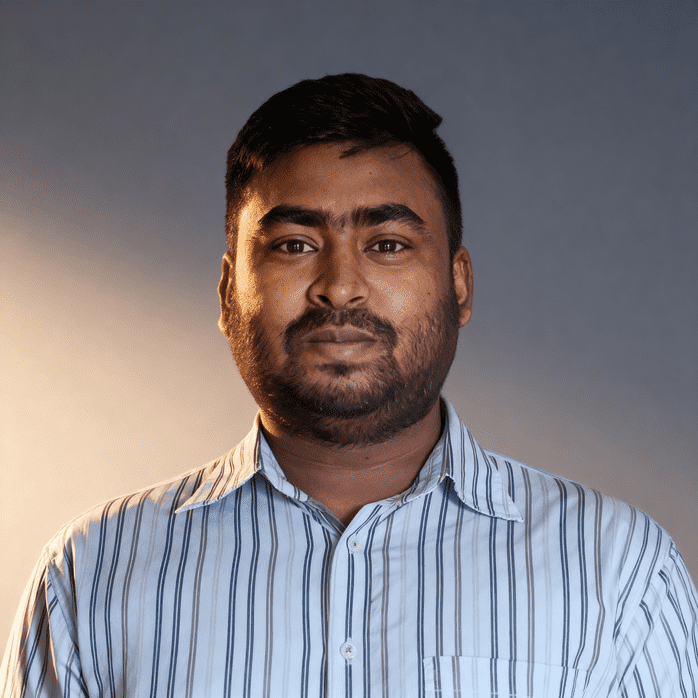
You’ll be working with me, Saddam.
Not an agency, not a project manager, not a junior who picked up your ticket. I read your message, I quote it, I build it, and I’m the one who answers when something breaks.
How do I know if my site is actually hacked?
Four signs are worth checking before you assume the worst.
Google shows pages you never made
Search site:yourdomain.com. If your site has twelve pages and Google shows four hundred, mostly pharmacy spam or text in a language you do not publish in, you have an answer.
Visitors see a warning, you do not
Once your browser has shown you the red warning and you clicked through, it stops showing you. Every new visitor still sees it. Check in an incognito window, or in Search Console under Security Issues.
Redirects, but only sometimes
Modern redirect malware ignores logged-in admins and often only fires for mobile visitors or people arriving from Google. If clients say the site sent them somewhere strange and you cannot reproduce it, believe them.
Admin accounts you did not create
Check Users. Any Administrator you do not recognize, especially one created at 3am on a day you were not working, is worth investigating.
More signs, including the easy-to-miss ones: How to tell if your WordPress site has been hacked.
What I actually do
Not a plugin scan. Here is the whole process.
Scan and diff against clean core
Every WordPress core file compared against the official release. Then plugins, themes, uploads and the database, with special attention to wp-config.php, .htaccess, index.php and functions.php.
Remove the malware
Malicious files deleted, injected code stripped from legitimate files, spam links and hidden content cleared from the database. The site keeps working while this happens.
Find the backdoor
Almost every real infection leaves a way back in, usually an ordinary-looking file in uploads or a few lines inside a plugin. Free scanners miss these. Leave it and you are reinfected in days.
Close the way in
Every password changed, unknown admins removed, everything updated, permissions fixed, unused plugins and themes deleted, XML-RPC closed if nothing needs it.
Get the warning removed
Review request submitted through Search Console once the site is clean. If your host suspended you, a written summary of what was found so you can get it lifted.
A written report you keep
What was infected, what was removed, where the backdoor was, how they most likely got in, and what to do next. Plain English, not a scanner log.
What it costs, and how long it takes
- Full scan and cleanup
- Backdoor hunt and removal
- Security hardening
- Google blacklist review request
- Written report
- 30 days of free bug fixes
Most cleanups are done within 5 to 7 days. If the site is actively serving malware to visitors, I start the same day I get access.
Get Your Site CleanedYou get the exact number in writing before I start, not after. If your case is standard, it is $497. If it is not, I will say so first.
What to send me to start:
- Your site URL
- WordPress admin login (a temporary account is fine)
- Hosting panel or SFTP access
- Anything you already noticed: warnings, redirects, host emails
Full pricing for everything else is on the pricing page.
Ask about a bigger cleanupWhy one person and not a service
You get me from the first email through to the report. Nobody hands your site to a junior, nobody reads you a script. I have been doing this since 2020 and a good share of the 350+ sites I have worked on arrived infected. Malware cleanup is pattern recognition, and the tenth time you see a backdoor style, you know where to look. See who you are actually dealing with.
About your credentials
I only ask for what I need, usually WordPress admin and SFTP or hosting panel access. Create a temporary admin account for me and remove it afterwards, and honestly I would suggest you do. Credentials are deleted when the work is done. You keep ownership of hosting, domain and site throughout.
After the cleanup
Rankings may dip while the site is flagged and usually recover over the following weeks once Google recrawls. Sites often get faster too, since injected malware runs on every page load. If it is still slow after cleaning, that is a separate problem and I can look at site speed as well.
Questions people ask
How long does malware removal take?
Most cleanups are finished within 5 to 7 days of getting access. If your site is actively infecting visitors, I start the same day. Complicated cases with multiple sites on one hosting account can take longer, and I will tell you that upfront.
How much does it cost?
A fixed $497 for a standard cleanup, including the scan, removal, backdoor hunt, hardening, blacklist review request and written report. Anything bigger than standard gets an exact quote in writing before work starts.
Can I just use a security plugin instead?
For prevention, a good plugin plus strong passwords and prompt updates goes a long way. For cleaning a site that is already infected, free scanners frequently miss backdoors, which is exactly why sites get reinfected after what looked like a successful cleanup.
What if it gets hacked again?
Every cleanup includes 30 days of free bug fixes, and that covers reinfection through anything I should have caught. If it comes back through a new vulnerability in something that was patched at the time, that is a new job, and I will tell you straight which of the two it was.
Will my site be down during the cleanup?
Almost never. I work on the live site with a full backup in place, or on a staging copy where the host supports it. If something has to come down temporarily, you will know before, not after.
Do I need to change hosting?
Usually not. Occasionally a site keeps getting reinfected because of another compromised site on the same account, and then moving is the real fix. I will tell you if that is what I find, even though it means less work for me.
What do you need from me to start?
Your site URL, WordPress admin access, and either SFTP or hosting panel access. Not sure how to get any of those? Send me what you have and I will walk you through the rest.
Amazing work! Everything was done perfectly and exactly as requested. Communication was smooth, fast delivery, and great attention to detail. I’m really happy with the result and would definitely recommend.
This is my second order and this time I was again pleased with Saddam’s work! He is very attentive and the communication is very good. I will certainly hire Saddam again for my next project!
Great professional, I hope to work with him more often. He delivers quickly and is attentive and concerned with the smallest details.
Prefer to start with a free audit?
Send your URL and get a specific list of what’s hurting your site within 48 hours, no obligation.
Get a Free Website & SEO Audit →